What would it take to trust an AI agent with your AWS and Azure workloads?
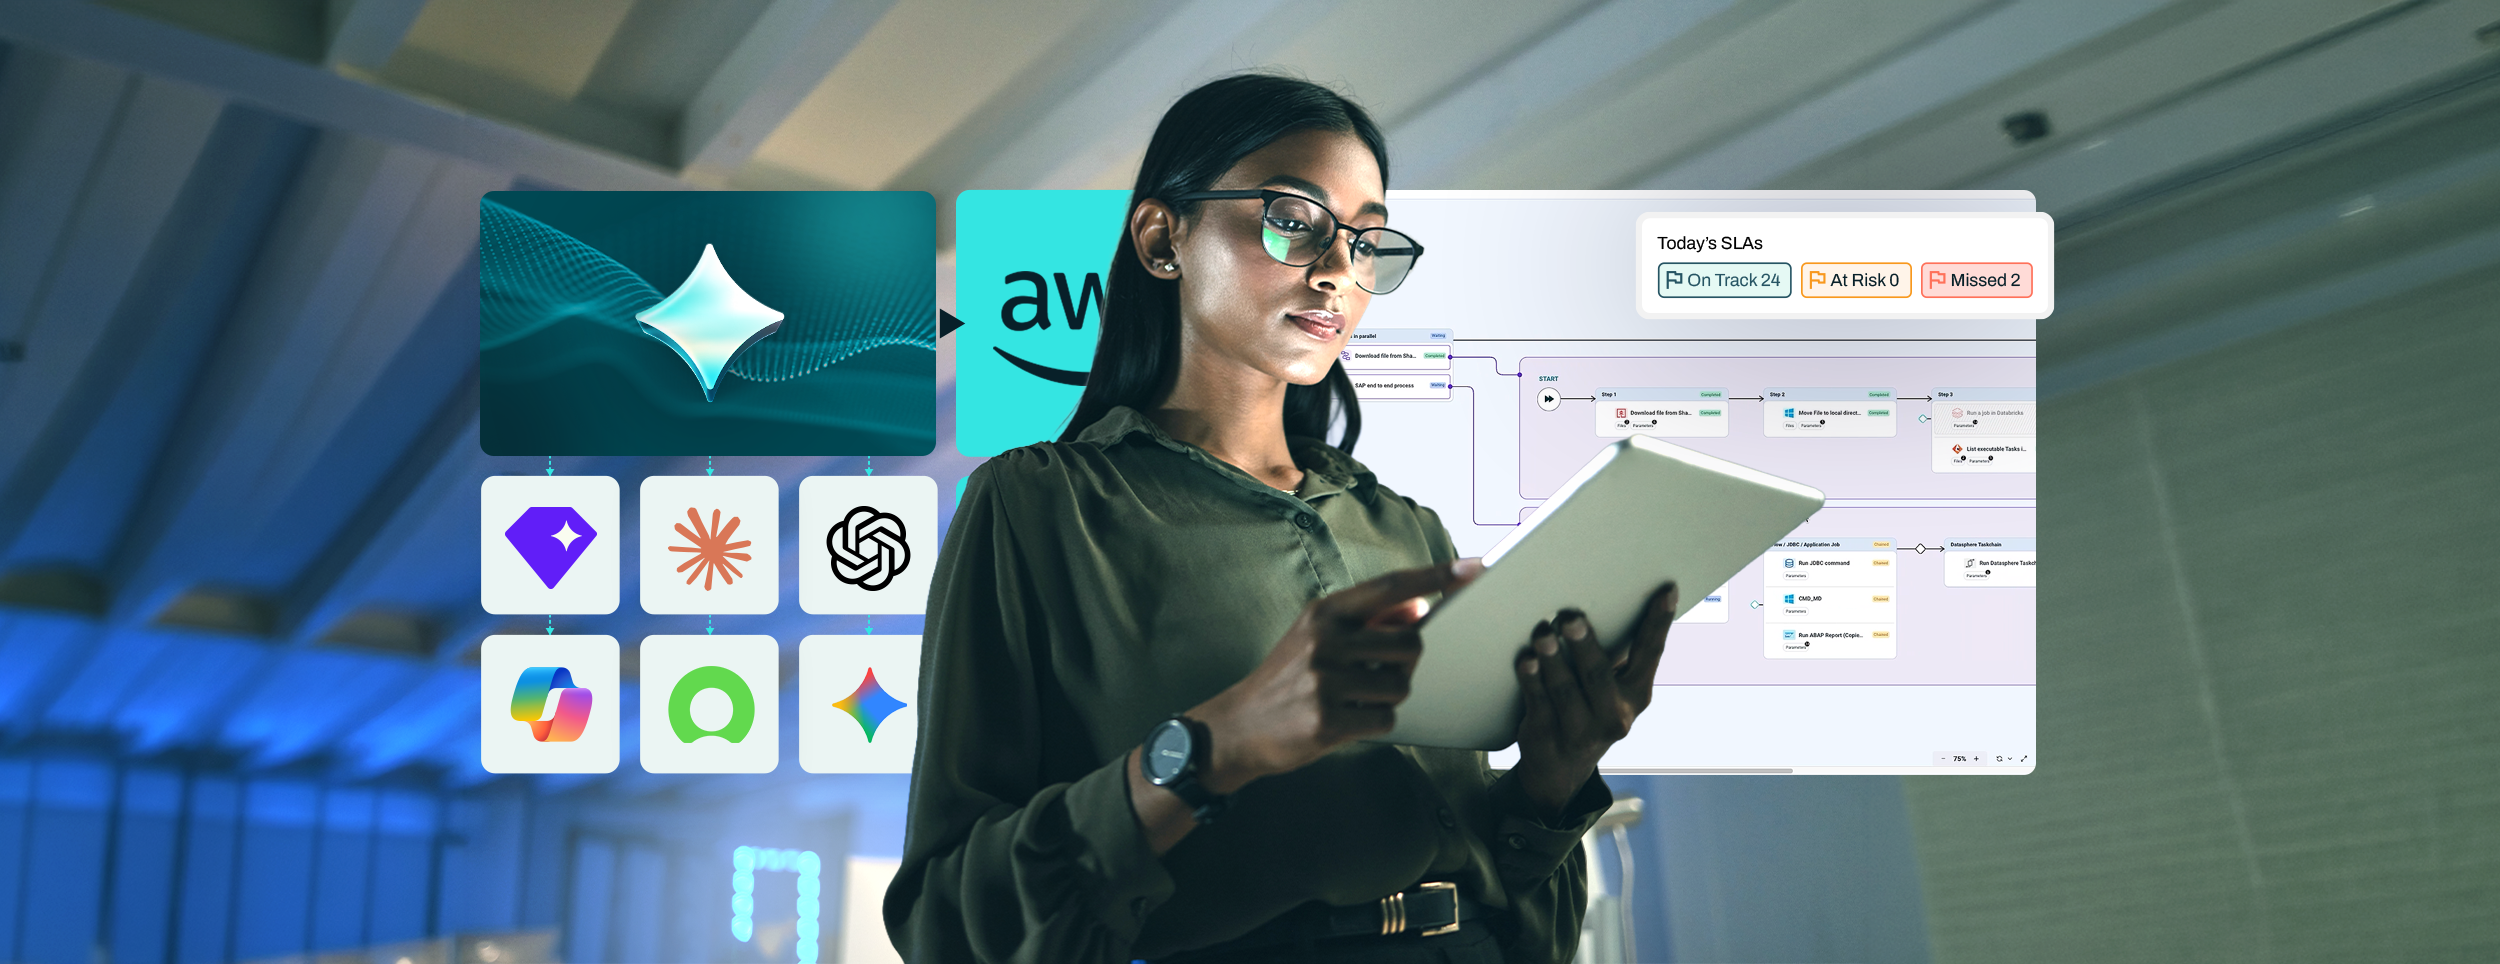
A business unit wants to put an AI agent on its fulfillment exception process. They’ve found a process with enough variance to justify AI, enough repetitive manual work to make automation attractive and enough business value to get leadership’s attention.
Now, they want sign-off from the architecture team, and not just for this agent. For any new agentic application.
You know that if you approve it, the next team will point to this decision. Then the next. Before long, one narrowly approved use case becomes the precedent for how agents act across your hybrid estate.
As you look through the proposal, you search for strong external controls on the agents, because you know that whether the agent is smart enough isn’t the issue. In a complex business process, an agent can reason perfectly and still become the riskiest participant in the chain if the architecture can’t prove what it touched, what it could’ve touched and what happened after it acted.
The precedent is bigger than the use case
Most AI governance conversations still start too close to the agent: with the model, the prompt, the runtime, the framework, the evaluation scores.
Those do matter, but they’re not the part you’ll be asked to defend when the agent triggers something downstream.
What you’re really approving is an execution model. Can an AI-powered decision leave the tool, cloud service or application where it originated and act safely across the systems that run the business?
For example, a fulfillment process may cross an ERP system, a warehouse platform, a data pipeline, a service management workflow and an on-premises dependency that’s been stable for years. Each domain has its own controls; each one can prove its own piece. But the business process doesn’t care where the boundaries are.
When a person works across that chain, they bring judgment and context with them. When an agent does it, the architecture has to supply the context, enforce the limits and preserve the evidence. If it can’t, you’re essentially approving a faster way to create an exception.
The chain was already complicated
You already know how these environments accumulate, in waves. These cloud migration waves move important workloads forward, but the execution paths underneath them don’t always modernize at the same pace. A polling job becomes the bridge, a script becomes the handoff and a temporary trigger becomes production infrastructure because the business keeps depending on it.
Take an order-to-cash path as an example: a bank file, an older scheduler, an ERP update, shell scripts, a cloud landing zone, an event rule, a transformation job and a warehouse load. None of those pieces is inherently wrong. The issue is that the process now spans multiple systems, teams and control planes.
When someone asks you to “agentify” that kind of process, you can’t avoid the architectural question: what can the agent decide, and what can your estate prove it’s safe to do?
Gartner predicts that more than 40% of agentic AI projects will be scrapped by the end of 2027. The surviving projects will not only have better agents, but also a governed path to production.
Proof of execution
Most teams aren’t training foundation models from scratch. They’re assembling agents from managed models, cloud AI services, copilots, agent frameworks, internal APIs and existing workflow logic. These agents may be able to reason through decisions, but the architecture still has to answer the questions that determine whether it can act:
- Who owns the workflow after the agent triggers it?
- Who is watching the process end to end?
- What exactly can the agent touch?
- Which steps require approval or validation?
- What dependencies have to resolve before execution continues?
- Can an in-flight action be stopped before it completes?
- Can security, legal and compliance prove what happened afterward?
Real trust in agentic AI comes from what the execution path can enforce: scoped identity, executable guardrails, downstream visibility, deterministic controls and an audit trail native to the workflow. The agent can evaluate options freely. What it can do in production shouldn’t expand because its reasoning sounded convincing.
Protocols standardize access; orchestration governs execution
Open protocols such as Model Context Protocol (MCP) and Agent2Agent (A2A) reduce the need to solve connectivity per agent, per vendor and per model update. But connectivity doesn’t settle the architecture question. Without a governed access point into the hybrid estate, each new agent arrives with its own identity decisions, logging assumptions, rollback plan and exception path. Pilot momentum can, therefore, turn into technical debt.
Orchestration carries the action from connection to completion, under the controls the business requires.
Give the agent a governed route
You don’t need a longer AI policy as much as you need a controlled execution path. AI agent actions should route through the same kind of layer that already governs critical workflows across cloud, enterprise applications, data platforms and on-premises systems.
That changes your review:
- The agent gets a governed interface, not a direct line to production systems
- Workflows exposed through MCP can be scoped to exactly what the agent is allowed to do
- The same access model used for human-triggered jobs can apply when an agent initiates the action
If an agent-triggered step needs to stop midstream, it should use the same control path as any other failed job, stuck execution or blocked dependency. Audit should work the same way: a byproduct of execution, not a separate reconstruction from scattered logs.
Before you sign off
So what do you tell the business unit this week?
Approving as-is is hard if the process underneath has no single place tracking what ran, what depended on what or how to stop the action midstream. Sending it back with no path forward only guarantees the same request will come from another team.
The approvable answer is conditional: route the agent’s actions through a governed orchestration layer before it touches the business process.
Then, human-triggered and agent-triggered steps can report through the same layer. The distance between “the agent decided” and “the work safely happened” closes because something sits between reasoning and execution, not because the agent got better at reasoning.
RunMyJobs by Redwood helps you build that governed layer, so you can orchestrate hybrid workflows across cloud, enterprise applications, data platforms and on-premises systems with the visibility, control and auditability agentic AI requires.
About The Author
Giampiero “Gp” De Ciantis
Giampiero “Gp” De Ciantis is a Director of Product Management at Redwood Software, where he leads product strategy and enablement for RunMyJobs’ agentic AI initiatives. Gp drives the roadmap and go-to-market for agentic orchestration, bringing together new technologies, platform architecture and customer requirements to make autonomous agents practical for enterprise automation.